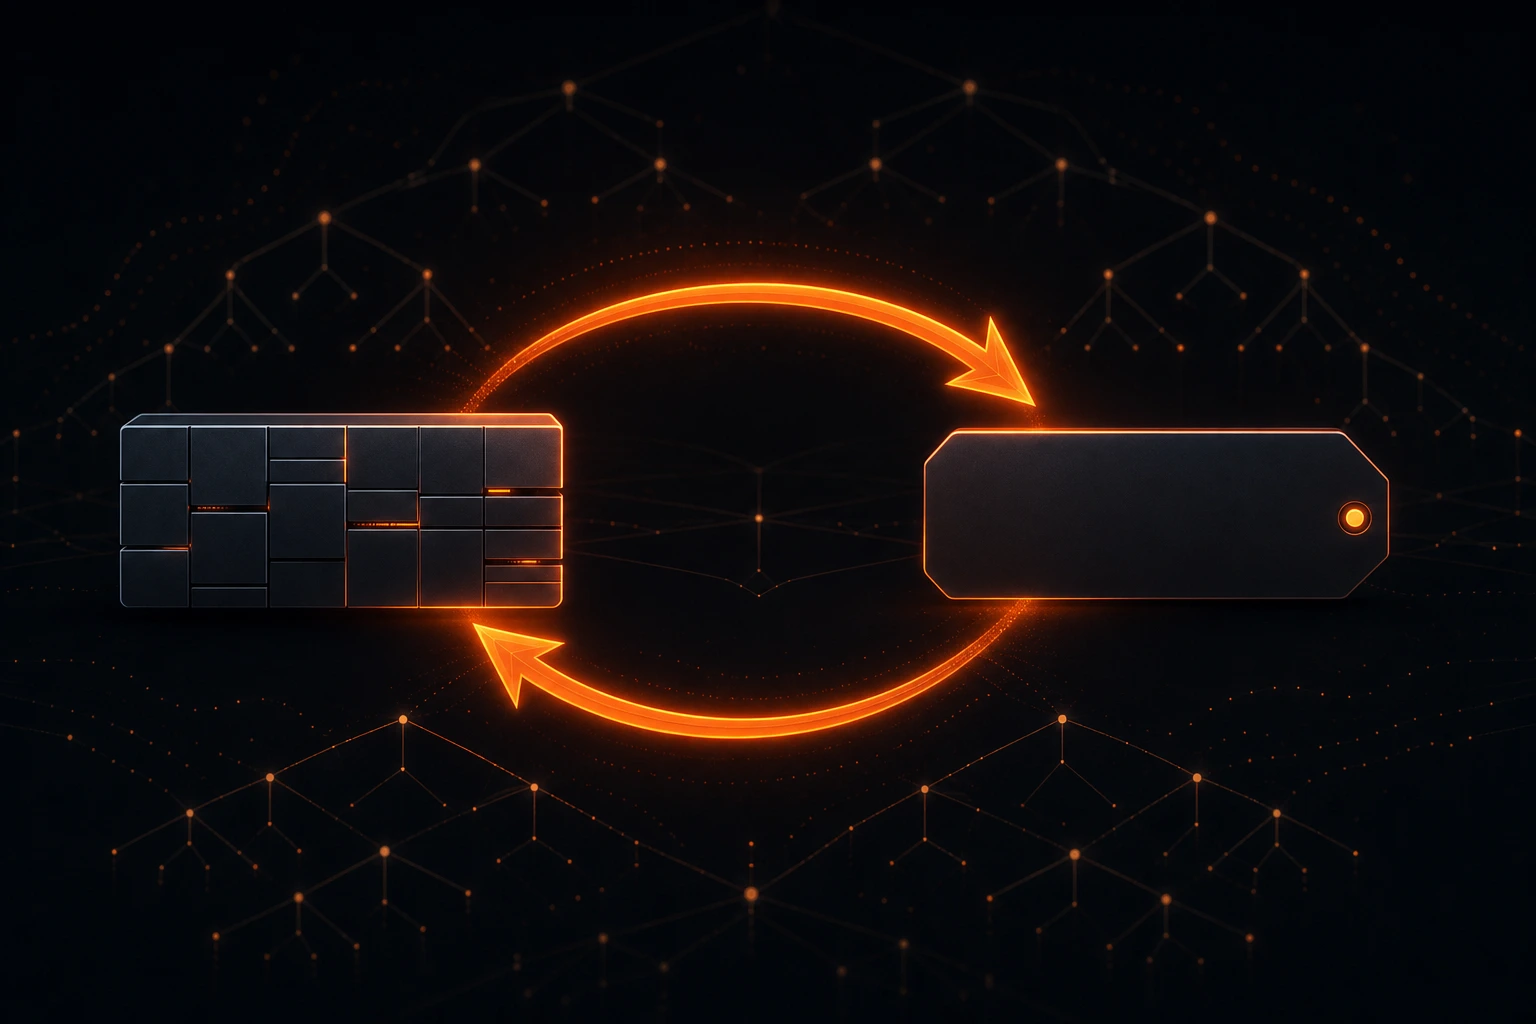
A reverse DNS lookup answers the opposite question from normal DNS: instead of "what IP address does this hostname point to?", it asks "what hostname is associated with this IP address?". A reverse DNS lookup is resolved through a special record type called a PTR record, and understanding how PTR records work explains a lot of otherwise confusing behavior - why your mail gets rejected, why your server logs show hostnames for some IPs and not others, and why you cannot fix your reverse DNS by editing your domain's zone file.
This post walks through the mechanics, who actually controls PTR records, and what reverse DNS is used for in practice.
How a reverse DNS lookup works: PTR records and in-addr.arpa
Forward DNS maps names to addresses: an A record says example.com is 203.0.113.7. Reverse DNS maps addresses back to names using PTR records (defined in RFC 1035), and it does so with a clever trick: it encodes the IP address itself as a domain name inside a special zone called in-addr.arpa.
To build the reverse name for an IPv4 address, you reverse the order of the octets and append .in-addr.arpa. For 203.0.113.7:
203.0.113.7 -> 7.113.0.203.in-addr.arpa
A PTR record at that name holds the hostname:
7.113.0.203.in-addr.arpa. IN PTR mail.example.com.
Why reverse the octets? DNS delegation works right to left: .arpa delegates to in-addr.arpa, which delegates 203.in-addr.arpa to whoever holds the 203.0.0.0/8 space, which delegates further down. Reversing the octets makes the most significant part of the address the highest level of the DNS hierarchy, so delegation can follow the same path as IP address allocation.
IPv6 works the same way but uses the ip6.arpa zone and reverses individual hex nibbles rather than octets. The address 2001:db8::1 expands to 2001:0db8:0000:0000:0000:0000:0000:0001, and its reverse name is:
1.0.0.0.0.0.0.0.0.0.0.0.0.0.0.0.0.0.0.0.0.0.0.0.8.b.d.0.1.0.0.2.ip6.arpa
Thirty-two nibbles, one label each. Nobody types these by hand - tools construct them for you.
Who controls PTR records (hint: not the domain owner)
This is the single most common point of confusion, so it is worth stating plainly: the holder of the IP address controls the PTR record, not the owner of the domain it points to.
Forward DNS for example.com lives in the zone you manage at your registrar or DNS host. Reverse DNS for 203.0.113.7 lives in the in-addr.arpa tree, which is delegated from the regional internet registries (ARIN, RIPE NCC, APNIC, LACNIC, AFRINIC) down to whoever the address block is allocated to - typically your hosting provider, cloud provider, or ISP.
In practice that means:
- On a VPS or cloud server, you set the PTR record in your provider's control panel or via their API, not in your DNS zone.
- On a residential connection, your ISP controls the PTR and you usually cannot change it at all.
- If you run your own address block, your RIR delegates the reverse zone to your name servers and you manage it like any other zone.
Editing your domain's zone file has no effect on reverse DNS. If you have ever added a PTR-shaped entry to a hosted DNS zone and wondered why nothing changed, this is why.
You can see who holds a given address block - and therefore who you need to ask for a PTR change - with a WHOIS lookup or an IP-to-ASN lookup.
What reverse DNS is used for
Mail server reputation. This is the big one. Receiving mail servers routinely look up the PTR record of every IP that connects to deliver mail. An IP with no PTR record, or a generic ISP-assigned one, looks like a compromised home machine rather than a legitimate mail server, and many receivers will refuse or heavily penalize mail from it. RFC 1912 states the expectation directly: every internet-reachable host should have a name, and PTR and A records should match. If you run outbound mail, a correct PTR is table stakes - we cover the full picture in How IP reputation affects email deliverability.
Logging and analytics. Web servers, SSH daemons, and log pipelines often resolve client IPs to hostnames to make logs readable. A line that says crawl-66-249-66-1.googlebot.com tells you more at a glance than the bare IP does.
Network debugging. traceroute resolves each hop's IP via reverse DNS, which is why you see router names like ae-1.core1.lon2.example.net in the output. Those names often encode location and role, which is genuinely useful when tracing a path.
A weak identity signal. Reverse DNS can hint at what an IP is - a datacenter, a residential line, a corporate gateway - but it is self-reported by the IP holder, so treat it as a hint, not proof.
Forward-confirmed reverse DNS (FCrDNS)
A PTR record alone proves very little, because the IP holder can point it at any name, including a domain they do not own. Forward-confirmed reverse DNS closes the loop with a two-step check:
- Reverse: look up the PTR for the IP. Say
203.0.113.7returnsmail.example.com. - Forward: look up the A (or AAAA) record for that hostname. If
mail.example.comresolves back to203.0.113.7, the check passes.
Passing FCrDNS proves that the party controlling the IP block and the party controlling the domain agree, which is much harder to fake than either record alone. Mail receivers weigh FCrDNS heavily; anti-abuse systems use it to validate claimed crawler identities (a bot claiming to be Googlebot should have a PTR under googlebot.com that forward-confirms).
How to do a reverse DNS lookup
On the command line, dig has a -x flag that builds the in-addr.arpa name for you:
dig -x 8.8.8.8 +short
dns.google.
Without -x, the equivalent explicit query is dig 8.8.8.8.in-addr.arpa PTR. To complete the FCrDNS check, resolve the returned name forward:
dig dns.google +short
8.8.8.8
8.8.4.4
The original IP appears in the forward answer, so 8.8.8.8 passes FCrDNS.
If you would rather not open a terminal, our free reverse DNS lookup tool does the PTR query for any IPv4 or IPv6 address in the browser, and the companion DNS lookup tool handles the forward side (A, AAAA, CNAME, MX, NS, TXT) so you can verify the round trip yourself. Neither requires an account.
Limits: what a missing or generic PTR really means
Reverse DNS is optional, and its absence means different things in different contexts.
- Many residential IPs have generic PTRs. Something like
x-203-0-113-7.dyn.isp.exampleis an auto-generated name covering an entire pool. It tells you the ISP, roughly, and nothing else. - No PTR at all is normal for end users. Plenty of consumer and mobile ranges simply have no reverse zone populated. A client IP without a PTR is unremarkable.
- No PTR on a mail server is a red flag. The same absence that is harmless for a browser is close to disqualifying for an SMTP client. Context is everything.
- PTRs are set by humans and go stale. Servers get reassigned and reverse zones do not always get updated. Never treat a PTR as authoritative identity on its own; forward-confirm it.
- One PTR per IP is the practical rule. Multiple PTR records for one address are technically legal but poorly supported, so an IP hosting fifty websites will still have at most one meaningful reverse name.
Reverse DNS also tells you nothing about where an IP is or who operates the network behind it. For that you want registration and geolocation data: The IP API's GET /v1/ip/{ip} endpoint returns location, ASN, and the operating organization for any address, which pairs naturally with a PTR lookup when you are investigating an unfamiliar IP in your logs.
Try it on your own infrastructure
Run dig -x against your mail server, your load balancer, and your own connection, and see what comes back - the results are often surprising. If you want to go further and enrich IPs with geolocation, ASN, and network ownership data programmatically, sign up for a free API key: the free tier includes 1,000 requests per day with no card required.